Immich is the best thing since freshly baked bread! I LOVE it, it’s not just a replacement for the techoligarks tools - I would say it’s even better. The local LLM/AI is amazing. You can just use phrases to look for your photos.
Proxmox is like being a kid in a free candy store. The helper scripts feel like cheating, you can get anything up and running in a breeze.
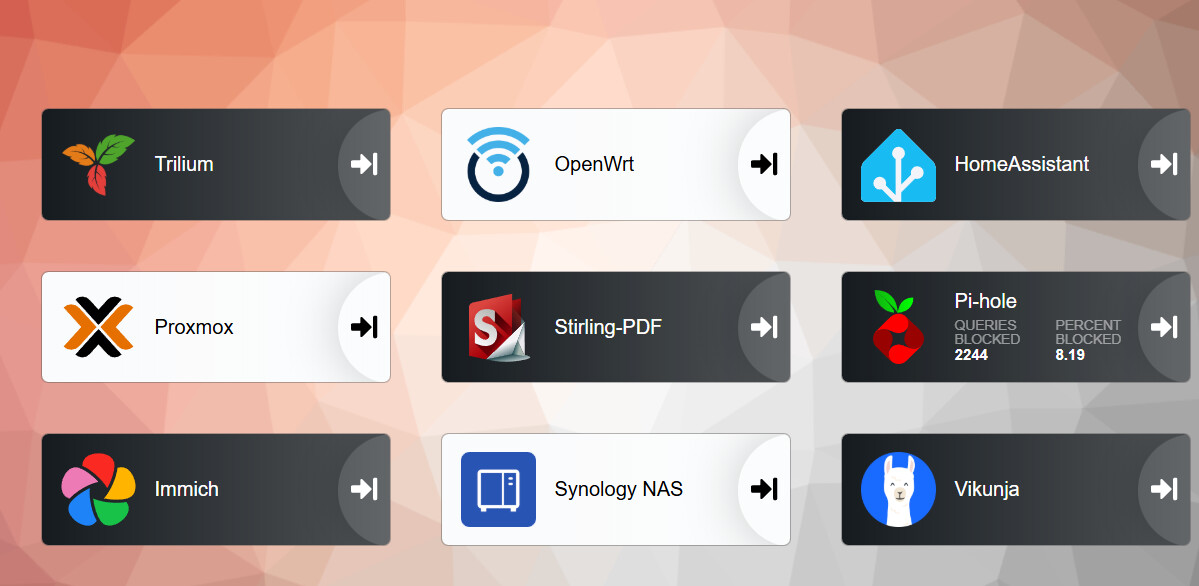
Here is my heimdall dashboard that I use for quick access to my vms and containers:
I really need to host a Vaultwarden on my Pi that runs PiVPN and Pi-Hole. But eeeeeh…
Hmmm….
Concerns over software security and validity of open source claim
Ventoy claims[7] to be an open source software and is hosted on GitHub open-source repository.[8] However, concerns have been repeatedly raised in various computing-related blogs[9][10][11][12][13][14] and forums[15][16][17][18][19][20][21][22][23][24]regarding the fact that source code tree contains a large number of pre-compiled blobs (binary executable files) of unknown origin, which makes it impossible or very difficult to audit the content of the software and ascertain that no malicious payload (e.g. backdoors) is being delivered. Additional concerns were raised in the same blogs and forums that the software appears to originate from China, that the software author has not responded to the concerns over the blobs for several years, that the identity of the author cannot be exactly established and that distribution of blobs without the corresponding source code could be a violation of GPLv3+ license the software claims to adhere to. Recommendations to migrate to alternative and more transparent open source software (e.g. Rufus, balenaEtcher) have been made in the same blogs and forum posts quoted above. Parallels have been drawn to recent vulnerabilities discovered in XZ Utils software.[19] On 7 May 2025 the author of the project has finally responded[16] to the concerns over the blobs, however response was limited to merely listing all the blobs along with build instructions, which other open source community members found very convoluted and difficult to reproduce.[10][20] No actions were taken by the author to eliminate blobs and replace them with the source code. The author has also responded to concerns that closed-source blobs can contain payload from Chinese government by merely stating that “[He has] never heard of the Chinese government forcing open source developers to install backdoors in their software. Just think about it, what benefits would this bring to the government, other than damaging its reputation?”.[16]
Yep. How much source code to Windows or MacOS do you get? Or sources for the binary blob of the embedded firmware for the radio in your home WiFi router?
It’s concerns all the way down. Do you have the source code to the compiler you use to build things? What if they built in a backdoor that recognizes when it is compiling the compiler in inserts the back door even if it isn’t in the source… and on, and on.
Do you get the source code to Etcher?
I agree, but the alternative is to carray around a dozen USB sticks. Is that better or worse?
Everyone has to answer that question from the point of view of their own risk posture and technical ability.
If you’ve scanned all the binaries with every available antivirus and antimalware tool and don’t get any hits, is that good enough?
Binary blobs are a huge problem (in my opinion, I guess) everywhere.
I just added the iso, booted and installed. Nice not to deal with trying to reformat a linux usb after etcher.
100% for Proxmox here. I have it setup on 2 small form factor PCs and clustered. Runs great no issues. All the usual items, HA server, jelly fin, Netbird node, MineCraft Modded server (Star Technology) etc etc.
I also use it for my day job and it saved the company unknown amounts of money over VMware in the 7 or so years I have had it setup. At the largest setup we had a 6 node cluster and had close to 100 VMs setup for both daily corporate use as well as test VM for the software development team. Have since moved to cloud only and still using proxmox on some servers we have rented.
One item to do on setup is edit the config and change it over to the community repo for updates.
Here is a script repository for a TON of useful scripts to setup all kinds of different services.
Also some good clean setup scripts to help get a good base to build from. Here is one I have used that deals with some of the good best practice items, like the repo item I talked about.
EDIT: Those links are different, just the preload image is the same for them.
But poke around, I am sure you will find all kinds of neat things to play with. Probably more than you have time to play with.  (If you’re like me at least)
Philip
Okay I think I have the helper script ran, updated, no nag, adguard, and automatic backups. Looks like I got the static ip’s set, but only time and a power outage will really tell.
So far so good!
Time for home assistant!
For all you home labbers, this channel is awesome!
you will find he likes xcp_ng more than proxmox, but covers both.
You will find alot here! Unifi recently dropped there os as downloadable, and you will find it covered there as well. I have always wanted to work with him, but he is in detroit, just too far for a commute!
I like his style, opens with a useful summary and the content is good. I have a feeling I will be watching a lot of those videos. thanks
I have watched for a very long time. He is tough to watch sometimes but usually stays right to point!
I have a lot to learn so I find myself revisiting a couple videos.
Let me know if i can help u ok.
Proxmox here. So easy, even I could do it. Burn the ISO on a stick, boot.
As others said, using proxmox helper scripts makes it easy. LabRax too but heavy lifting done on servers below. While they say 3 node is ideal, I only run 1 node in prox but have 3 backups.
Nice thing is if you screw up a config under proxmox, you can always destroy and start over.
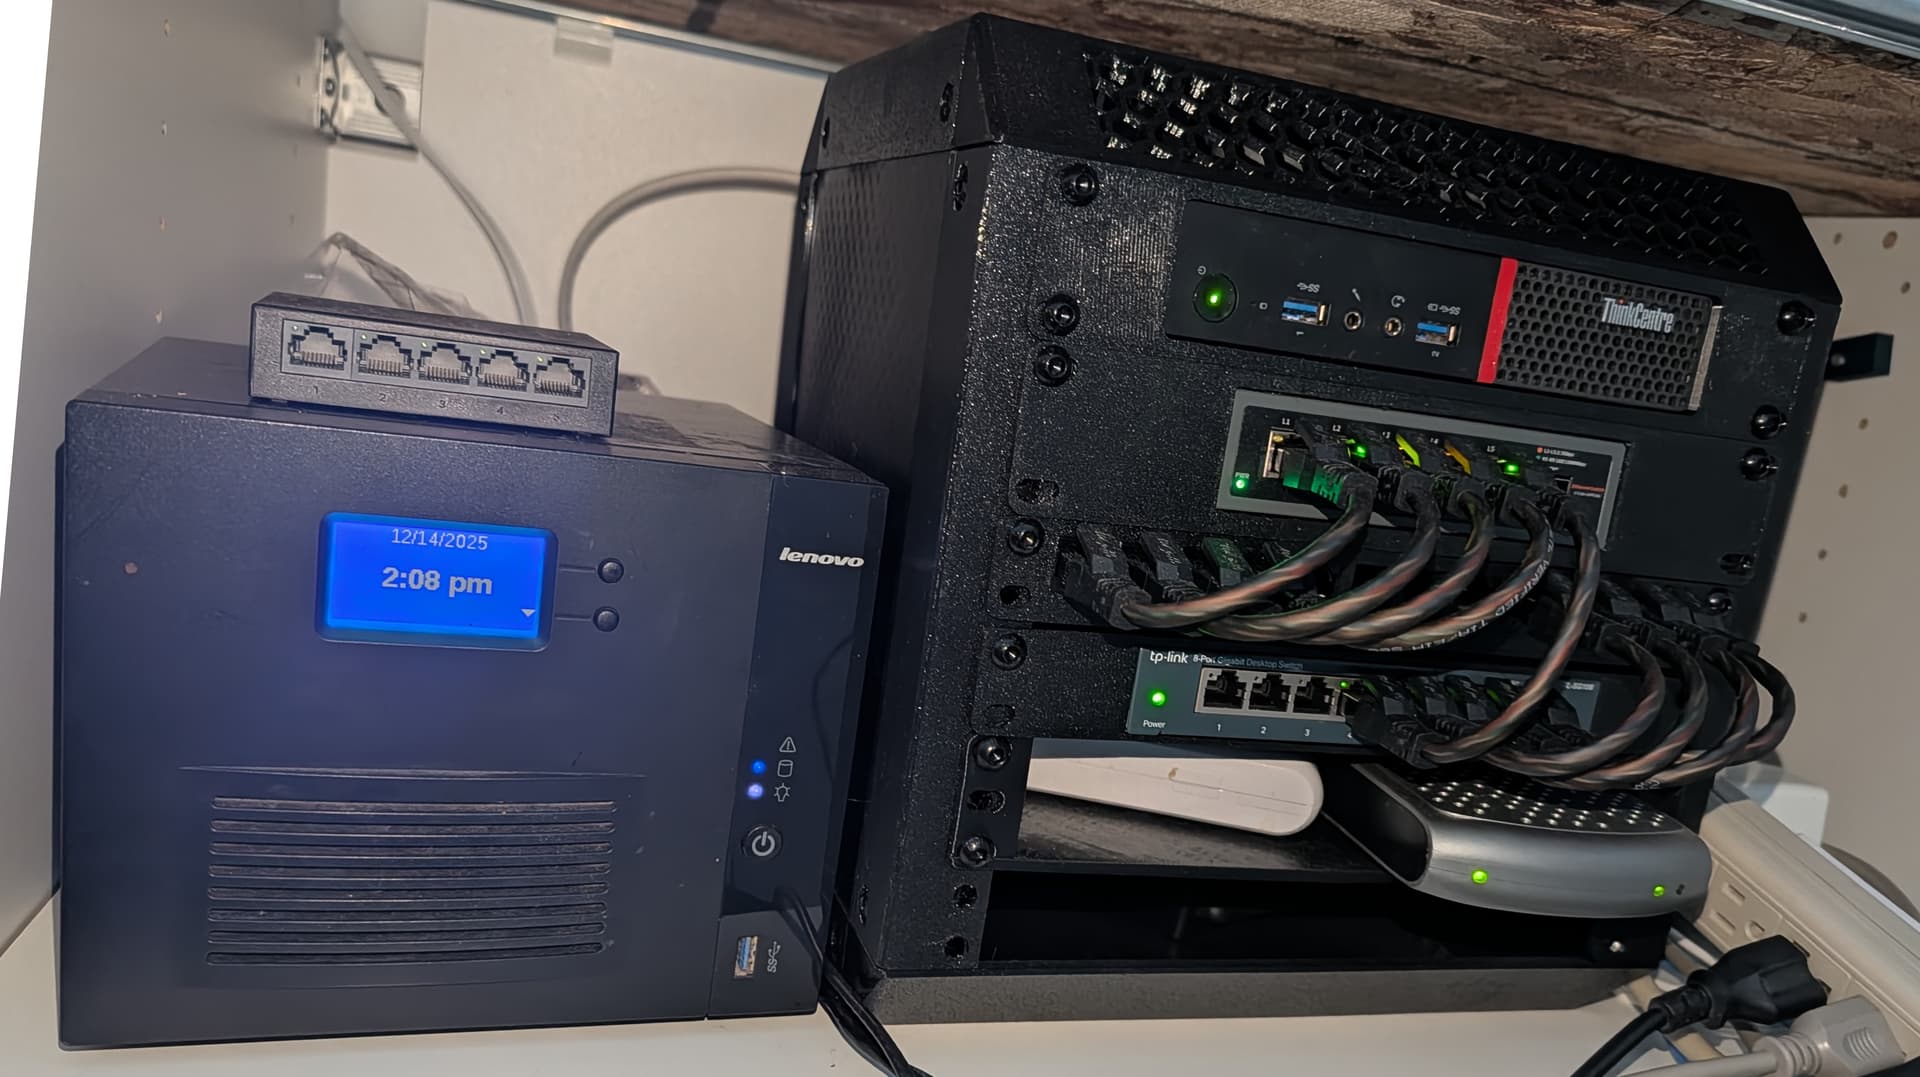
Currently running HA, OMV , Channels, Docker & AgentDvr. The little lenovo is planned for dns, pi.hole & stuff.